
Security, Governance, Risk
AI Governance, Cybersecurity & Enterprise Risk for CIOs
Jyoti Ponnapalli, VP of Applied AI at Frontier Communications, on why swarms of AI agents that can answer differently every time force the guardrails into the orchestration layer.
Roderick D. Harris, Principal at RDH Strategic Advisors, said controlled pilots should be the front door for new AI.

Lead Enterprise Architect Philip Flint on why CIOs must govern delegated authority, not just access, as AI agents inherit the power to act at scale.
Global Technology Executive Eswaren Allaghery on why enterprises keep stacking AI governance onto compliance regimes that already overlap.

Platform Architect Harshavardhan Peddireddy on why generated outputs still carry customer data, and how a tracking key that travels through every pipeline makes a consent withdrawal actually land.

Lester Godsey, CISO at Arizona State University, on how security became a strategic accelerator for one of higher education's most ambitious AI deployments.

Ricardo Bastos, Cybersecurity Engineering Manager at TELUS, on how AI exposes weak governance and called for measurable impact rooted in business context.

Anmol Agarwal, Senior Security Researcher at Nokia, on prioritizing value-first AI grounded in real-world security operations.
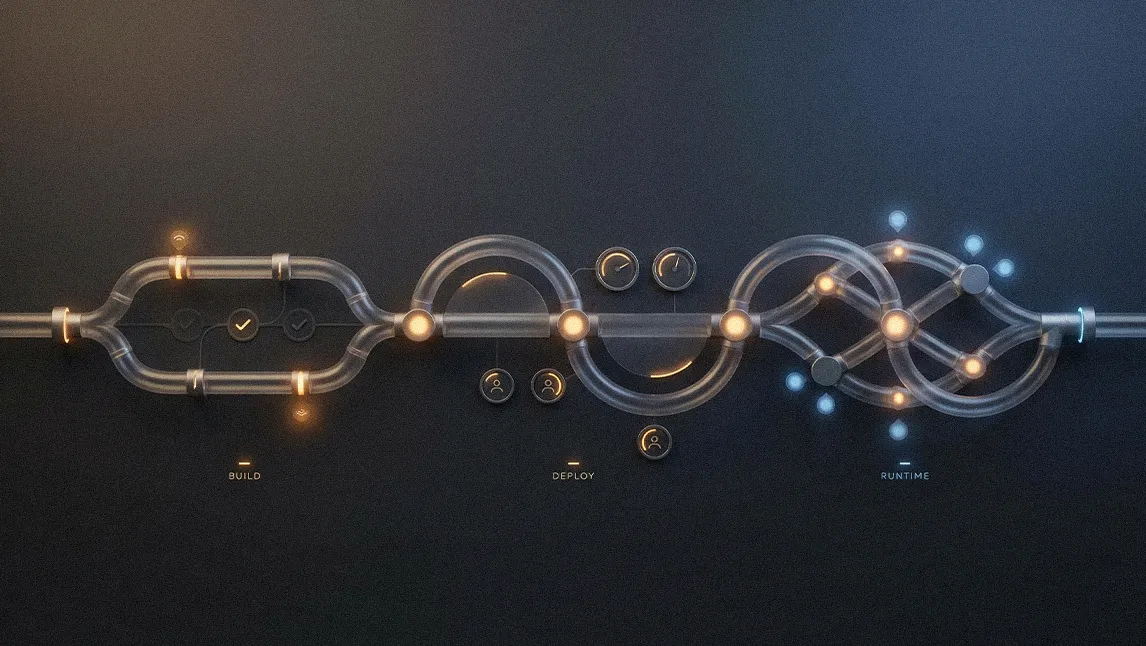
Wells Fargo’s Siva Paramasamy on why AI governance now succeeds or fails at the pipeline level, not in policy, as models and agents move into production.

Robin Patra, Head of Data, Analytics & AI at Keeley Companies, on a three-pillar playbook for enterprise AI success rooted in governance excellence.

A report from Palo Alto Networks warned that the popular open-source AI assistant Moltbot is inherently insecure for enterprises.

Glyn Bowden, Senior Distinguished Technologist at HPE, outlined how enterprises can move agentic AI from personal wins to scalable systems through business-first governance and experimentation.
Amit Basu, VP, CIO & CISO at International Seaways, on how AI-driven fraud targets human behavior and why identity, verification, and leadership now define cyber resilience.
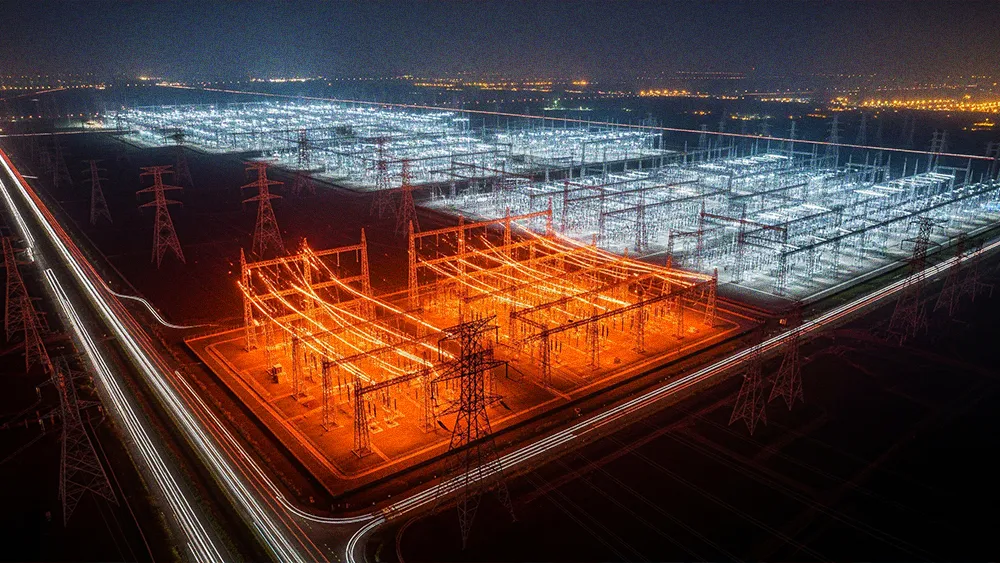
Ann Dunkin, Distinguished Professor at Georgia Institute of Technology, framed energy reliability as a CIO-owned strategic risk as AI demand collides with grid instability.
Bill Willis, CTO and Head of Advisory at IDMWORKS, on how healthcare IAM breaks when single identities meet multi-persona reality and why orchestration restores access, security, and care.

Ed Gaudet, CEO and Founder of Censinet, discusses how always-on vendor AI is expanding healthcare risk after deployment.

David Cross, CISO of Atlassian, on how enterprises are becoming AI-native by embedding security, governance, and human oversight into intelligent workflows.