A Coherent Management System Keeps Enterprise AI Governance From Fragmenting
Eswaren Allaghery, Head of Information Technology at IBL Seafood Hub, on why enterprises keep stacking AI governance onto compliance regimes that already overlap.
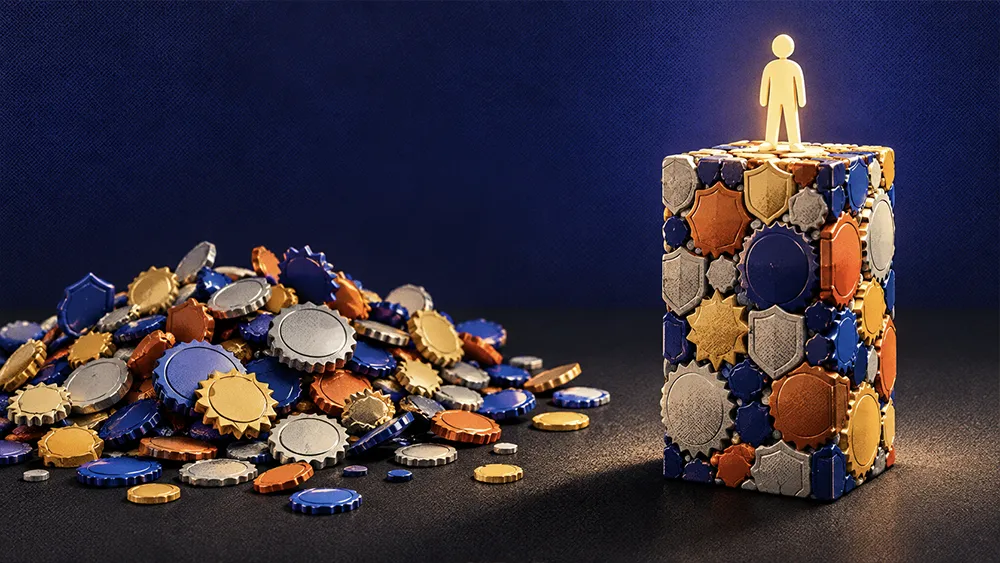

Over the past decade, enterprise technology leaders have accumulated layers of standards, regulatory requirements, and compliance frameworks. A security standard here, a privacy regulation there, an industry control stacked on top, each one arriving with its own owner, its own evidence, its own audit trail. Now artificial intelligence is landing on that accumulated pile, and the instinct is to bolt on one more governance layer to keep it in line. The more durable move runs the other way. Reconcile the overlap that already exists through an Integrated Management System, and AI has somewhere coherent to stand before the first agent ever ships.
Eswaren Allaghery is a Global Technology Executive and Certified Global CIO with more than 18 years of international experience leading enterprise technology across manufacturing, media, telecommunications, hospitality and business services on five continents. Most recently, he served as Head of Information Technology at IBL Seafood Hub, the integrated seafood cluster within IBL Group. Earlier, within Omnicom, he built and scaled global IT for a Digital & Software Centre of Excellence and led the alignment of thousands of endpoints, enterprise applications and security standards across international operations. An ISO 27001:2022 Lead Auditor, he has spent much of the past two years working through audits, compliance reviews and regulatory requests across complex operating environments. That experience reinforced his view that the challenge is not simply adding more controls, but creating coherence across the ones already in place.
"When every request comes in through its own silo, it gets blurry. You can give people a process and they’ll follow it, but gaps can remain, and that’s where security and privacy risks can emerge. I wanted something more coherent, something that speaks to everyone and puts everyone on the same stage," Allaghery said.
The idea itself isn't new. Integrated Management Systems have long been used within Quality and Compliance to bring multiple standards, certifications and operational requirements into a more coherent structure. But those requirements rarely sit inside one function. A diversified organization may have standards and controls covering food manufacturing and handling, port operations, guest services, finance, technology, cybersecurity, privacy and other areas of the business. Each function may have different obligations, but the organization still needs a consistent approach to interpreting requirements, establishing procedures, assigning accountability, escalating issues, and demonstrating that controls are implemented and operating as intended.
Allaghery’s argument is that organizations can extend the principles of an Integrated Management System across diverse operational and technology domains, allowing new areas such as AI governance to fit into an existing enterprise structure rather than becoming another standalone silo. "The objective is not to make every department work the same way. It is to establish a common approach to understanding, interpreting and acting on requirements," Allaghery said. "A technology professional supporting a hospitality operation should be able to understand how a service procedure is structured, just as someone in finance should be able to understand the controls and responsibilities around using a generative AI tool. The subject matter may change, but the underlying management approach should remain coherent."
That structural choice can determine whether AI governance is built on a coherent foundation or layered onto fragmented, overlapping, and potentially inconsistent controls.
Overlapping standards: Compliance requirements tend to accumulate in layers. A security standard here, a privacy regulation there, then an industry requirement layered on top, each potentially bringing its own controls, owners, evidence requirements, and audit trail. "Many of those requirements end up asking similar questions, but at different levels of detail or from different perspectives. You may be dealing with ISO 27001, ISO 9001 and other management standards, NIST, TISAX, SOX, GDPR, cyber insurance requirements, internal and external audits, and other industry or regulatory mandates. They are not the same and do not serve the same purpose, but there is often significant overlap in the risks, controls, evidence requirements and accountability they expect organizations to address."
Deduplicate and synthesize: The system acts as a translation layer for organizational priorities, translating the board’s view of which risks matter most into terms that each level of the organization can understand and act on. "An Integrated Management System should not eliminate those standards or the way of working. It should help reduce duplication, identify and address inconsistencies, and provide a structured way of communicating priorities and information from top management to the operational level, while ensuring that feedback from operations flows back up to management." The point is not to replace the individual standards, certifications or operating procedures. It is to reconcile where they overlap, preserve where they differ, and give the organization a coherent way of understanding what is required, who is accountable and how information moves through the business.
A playbook that traveled: Years before AI, Allaghery’s team was supporting digital platforms for competing global clients in the same industry across Costa Rica, Mauritius and India. Each client had its own dedicated environment, teams, access controls and data boundaries. No team could move into another client’s environment, and no client’s data could cross into another’s, while corporate security requirements and each client’s own industry controls had to hold at the same time. "We had to meet our own corporate requirements and each client's requirements at the same time. We developed documentation and ways of working that gave people the information they needed to do their jobs, while keeping responsibilities, access and data properly segregated. What started as a practical solution became a repeatable way of working that we could apply in other client environments," he said. The lesson was not that every client should operate identically. It was that different requirements could still be governed through a common management structure while preserving the segregation, controls and responsibilities unique to each environment.
None of this was designed for AI. It predates the current wave by years, which is exactly why Allaghery trusts the principle. He has watched a similar pattern emerge before with the internet, IoT and blockchain: a new generational technology arrives, organizations are under pressure to adopt it quickly, and the governance scramble can begin before there is agreement on how it should fit within existing business processes and controls.
When an organization’s requirements and controls are already aligned through a coherent management structure, new technology has a foundation to build on. When they aren't, AI risks becoming another layer on top of existing silos, potentially compounding the fragmentation that was already there.
Clean reports, wrong numbers: Here the same fragmentation surfaces in the data. When underlying business processes are not consistently defined or executed, the data they generate can become inconsistent. AI placed on top of that data does not automatically resolve the problem; it can accelerate and amplify whatever it inherits, good or bad. "The system was good. It was the process that wasn't well defined, so the data wasn't coherent," he said. "When we put AI on top, it produced reports that looked good but were completely different from what they should have been, and without the people in the middle to catch that, it goes straight out." That is where the Integrated Management System becomes more than a compliance structure. It provides a common framework for establishing how processes are governed, where accountability sits, how exceptions are handled, and how issues and feedback are escalated. The technology may change, but the need for coherent process ownership does not. The example also exposes a second problem: when AI produces an output, who is accountable for deciding whether that output is accurate, usable and appropriate?
No single owner: AI does not consolidate accountability into a single new owner. Technology teams may provide the platform, architecture, security controls and technical governance, but they cannot own the business process or its outcome on behalf of the functions using it. The training that enables people to use the technology effectively, the processes each team operates, the controls around how the tool is used, and the responsibility for determining whether it delivers the intended outcome ultimately sit across the functions and individuals accountable for those activities. "The operations team owns their process and has to be accountable for it." An Integrated Management System makes that distribution of accountability visible. It provides a common structure for defining who owns the process, who owns the control, who provides the technology, who approves exceptions and how issues are escalated through the organization.
When those responsibilities are clear, AI governance becomes less about adding another control layer and more about integrating new capabilities into the way the enterprise already manages risk, performance and accountability. The feedback flowing up and down the organization also creates a basis for continuous improvement, allowing processes, controls and ways of working to evolve as new risks, technologies and operating needs emerge.
The burden of repeated compliance activity is real, but Allaghery treats it as a symptom. The condition underneath is fragmentation, the organizational kind, where every team answers the same questions in its own dialect and nobody reconciles the answers.
Address that fragmentation, and AI has a more stable governance foundation before the first agent ever ships. "At the end of the day, a coherent management system gives value back to the business," he said. "Instead of everyone chasing the next auditor, the next certification or the next control request, you keep everyone knowledgeable, accountable where they need to be, and still meeting the criteria."
The result is not fewer standards or less governance. It's a more coherent way of managing them—one that gives AI, and the people responsible for it, a clearer structure for making decisions, escalating issues, continuously improving how work is done, and creating value.

If this caught your attention, that’s not accidental.

The best editorial systems don’t happen by accident. Outlever builds them.